Logs from Filebeat to Logstash to Elasticsearch – 3

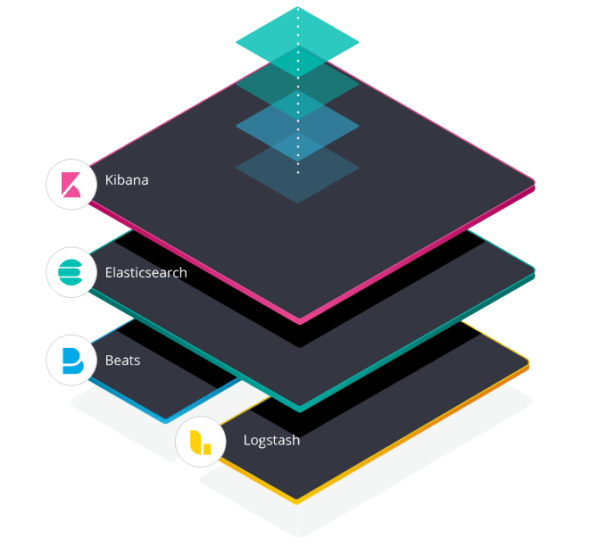
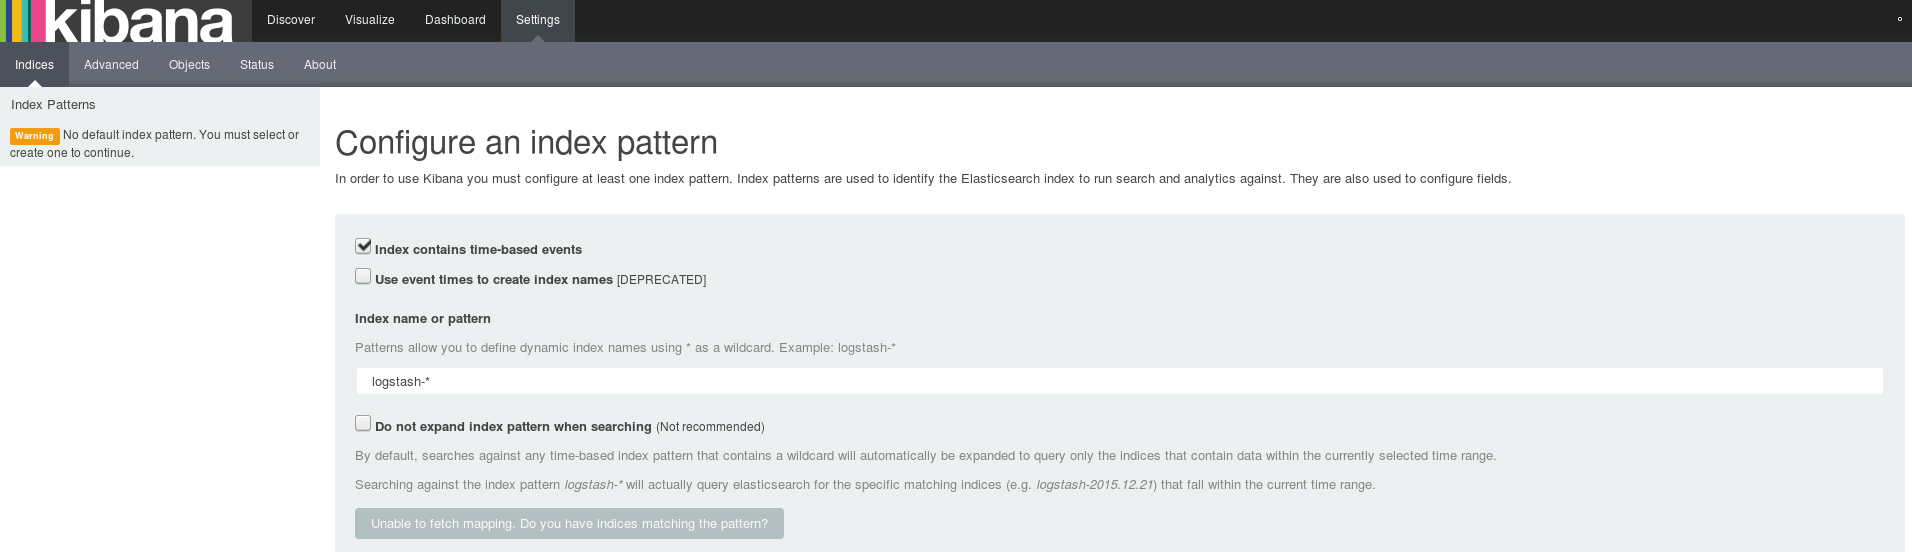
We sow together how to install and configure Filebeat, Logstash and Elasticsearch. Our log data has been sent from Filebeat to Logstash, then forwarded to Elasticsearch. In this blog, we will see how to configure Kibana and discover our data. Data Stream vs Index A data stream lets you store append-only time series data across multiple indices while giving you…