

by Alexandre Nestor
In the previous article A step by step guide to install and configure OCI client the oci client configuration.
OCI provides also token access.
~ > oci session authenticate --profile-name MY_SESS_PROF --region eu-zurich-1 --tenancy-name <your tenancy name>
    Please switch to newly opened browser window to log in!
    You can also open the following URL in a web browser window to continue:
https://login.eu-zurich-1.oraclecloud.com/v1/oauth2/authorize?action=login&client_id=iaas_console&response_type=token+id_token&nonce=b020c2c3-0027-4223-85fd-23203c01023c&scope=openid&public_key=eyJrdHkiOiAiUlNBIiwgIm4iOiAidTl5MENMLWxsSWpIbElsd2Nw**************************VprV0dHbzJLRE5yY2pvbEQ4S0xXTkducGN5OG9tTkh5R0RZaEI1R2VPMF9KbWhMNjVvSTlrZEtrZHp1NHdRRXpnSEZlUXFYQ2NTc1hyUWl3N0I4b25VYWZLc0h5Y2tnNWUtMUdlNWtlZVNZSlJRaVJ1c0hrdHdackh1Q3Z4UnJmOW0wVVNRIiwgImUiOiAiQVFBQiIsICJ*******************9&redirect_uri=http%3A%2F%2Flocalhost%3A8181&tenant=*************
    Completed browser authentication process!
Config written to: /Users/mytest/.oci/config

    Try out your newly created session credentials with the following example command:

    oci iam region list --config-file /Users/mytest/.oci/config --profile MY_SESS_PROF --auth security_token
Note: The tenancy name can be found on the page “Tenancy details“
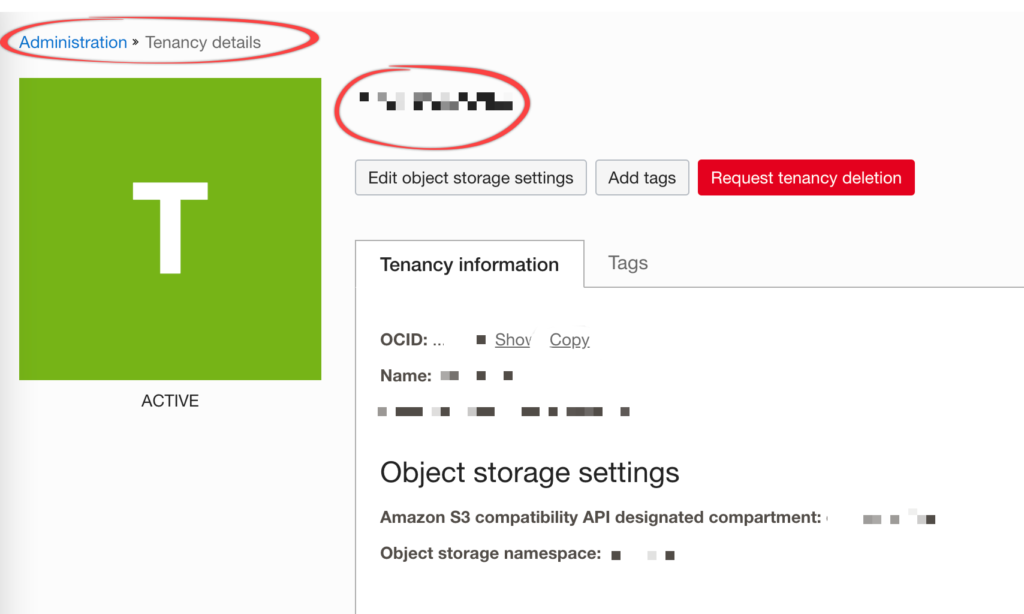
Let’s try out the OCI output suggestion:
oci iam region list --config-file /Users/mytest/.oci/config --profile MY_SESS_PROF --auth security_token

{
  "data": [
    {
      "key": "AMS",
      "name": "eu-amsterdam-1"
    },
    {
      "key": "ARN",
      "name": "eu-stockholm-1"
    },
......
The $HOME/.config file was updated with the token and the session parameters are in the session directory as follows:
Questions about your own setup? A dbi services consultant can look at your case.
Talk to an expert (opens in a new tab)
~ > cd $HOME/.oci
.oci > tree
.
├── config
├── oci_api_key.pem
├── oci_api_key_public.pem
├── rsa.private
├── rsa.public
└── sessions
    └── MY_SESS_PROF
        ├── oci_api_key.pem
        ├── oci_api_key_public.pem
        └── token

.oci > cat config
[DEFAULT]
user = ocid1.user.oc1..aaaa*********wyqwklitkuu6owpzcj****
fingerprint = 01:**************:3c:9a:99:ff:08:******
key_file = ~/.oci/oci_api_key.pem
tenancy = ocid1.tenancy.oc1..aaaaaaaa**************iai4di356quiofira
region = eu-zurich-1


# Here the new added session
[MY_SESS_PROF]
fingerprint=20:25:**************e:aa:00:c6
key_file=/Users/mytest/.oci/sessions/MY_SESS_PROF/oci_api_key.pem
tenancy=ocid1.tenancy.oc1..aaaaaaaac5*************s5bgmciai4di356quiofira
region=eu-zurich-1
security_token_file=/Users/mytest/.oci/sessions/MY_SESS_PROF/token
For an easy use these env variables are available to avoid passing --profile and --auth parameters on oci command line:
~ > export OCI_CLI_PROFILE=MY_SESS_PROF
~ > export OCI_CLI_AUTH=security_token
Token validation:
~ > oci session validate  --profile MY_SESS_PROF --auth security_token
Session is valid until 2022-10-06 17:59:00
The token can be refreshed before it’s expiration:
~ > oci session refresh --profile MY_SESS_PROF
Attempting to refresh token from https://auth.eu-zurich-1.oraclecloud.com/v1/authentication/refresh
Successfully refreshed token
~ > oci session validate  --profile MY_SESS_PROF --auth security_token
Session is valid until 2022-10-06 18:16:42
Hi
Never had this error.
I guess you already check the paths, the rights on the files.
Add -d option on your command line for debug traces.
Hi Alexandre,
I’m using the same approach from a Guthub workflow and the oci session validate command fails on my side:
Guthub workflow steps:
run: actions/setup-python@v4 with python-version: “3.10”
run: python -m pip install oci-cli
run: echo `oci –version` –> oci version 3.39.1
run: oci session authenticate –no-browser –profile-name GITHUB_DEV –session-expiration-in-minutes 60
#no error on ‘oci session authenticate’ run, config file updated with a new [GITHUB_DEV] section
[GITHUB_DEV]
fingerprint=***
key_file=/home/ubuntu/.oci/sessions/GITHUB_DEV/oci_api_key.pem
tenancy=***
region=***
security_token_file=/home/ubuntu/.oci/sessions/GITHUB_DEV/token
run: oci session validate –config-file /home/ubuntu/.oci/config –profile GITHUB_DEV –auth security_token
# ERROR
# No security_token_file was found in config for profile: GITHUB_DEV
Do you have any hint ?
The same commands executed at command line from my local oci cli work well …
Thanks
nuvoladev