Skip to content

Security

Email Spoofing

Have you ever had this unhealthy sensation of being accused of facts that do not concern you? To feel helpless in the face of an accusing mail, which, because of its imperative and accusing tone, has the gift of throwing us the opprobrium? This is the purpose of this particular kind of sextortion mail that uses spoofing, to try to… 
Documentum CS 7.* – 777 permission on jobs log

A few weeks ago at a customer, our team was involved in a security control. We tracked files with 777 permission and we detected that logs generated by Documentum jobs have 777 permissions. Security before anything else, that’s why this topic was my top priority! First of all, I checked the logs on some Content Servers, and I had the… 

SQL server security pre-conference @SQL Pass Summit 2018 in Seattle

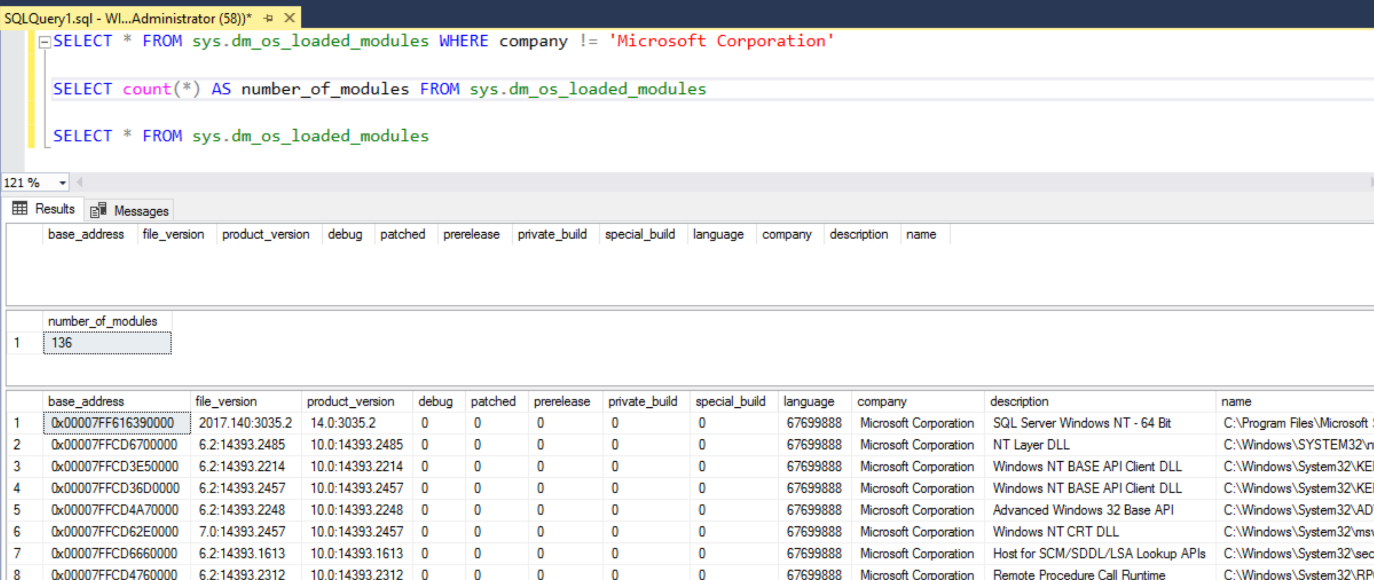
After long hours of flights, Christophe Cosme and I finally arrived in Seattle at the SQL PASS Summit 2018. We picked up our badge and bag and now we are ready to begin… This first day for me started with the pre-conference about SQL Server Security with Denny Cherry. Many topics were discussed like: Network Designs (such as public IP… 

SQL Server Tips: Drop a database-user attached to a service…

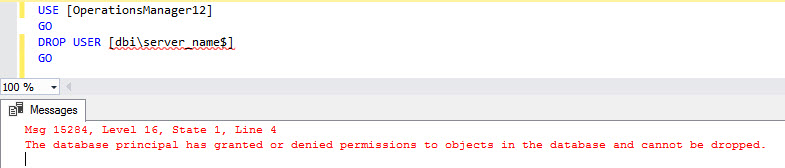
Few weeks ago, I have a little issue when I try to drop a database-user without login Unfortunately, I do a little mistake at the beginning… I receive like every morning a report if all AD logins (computers, groups, users) registered on SQL server instances are in the AD with the useful command sp_validatelogins This report indicates that a computer… 

SQL Server Security: Are your databases ready for the GDPR?

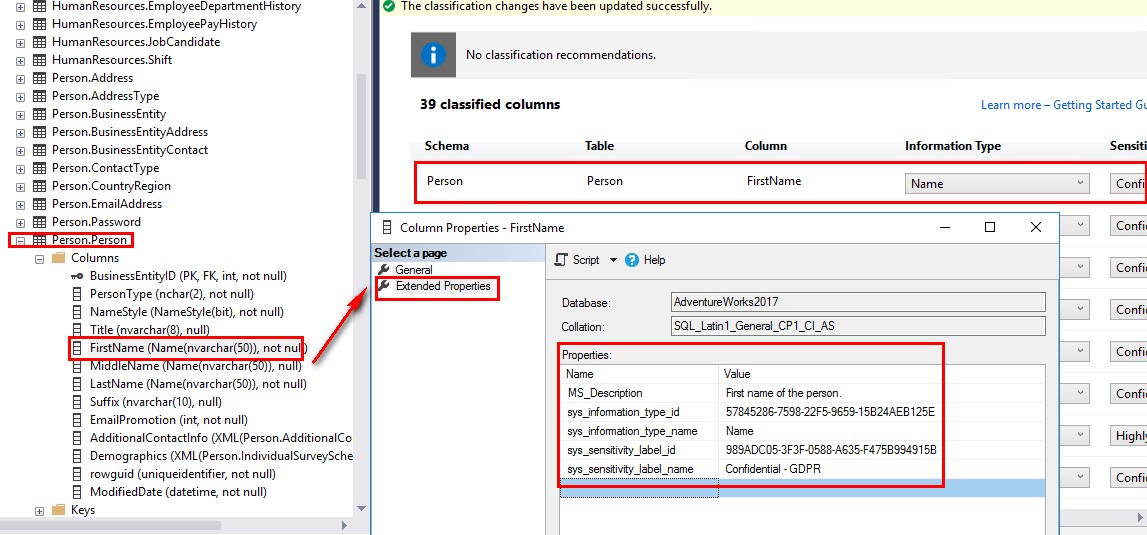
The GDRP (General Data Protection Regulation), voted in 2016, will be applied in the European Union soon (May 25, 2018). We heard a lot of this new directive. The goal is to improve the protection and confidentiality of personally identifiable information for every European citizen. Quid of Switzerland? Read the article of Gregory here. A personal data is information that… 

Keep your orapw password file secure

By Franck Pachot . This is a small demo I did when I’ve found a database password file (orapw) lying around in /tmp with -rw-rw-rw- permissions, to show how this is a bad idea. People think that the orapw file only contains hashes to validate a password given, and forget that it can be used to connect to a remote… 

Pass Summit 2017: how to bypass SQL Server security

Last Friday I saw a very interesting session in Pass Summit 2017 about how to Bypass, or Ensure, SQL Server security by Matt Martin. Matt explained us how to bypass SQL Server security with the complicity of your SQL Server DBA. Msdb is the most powerful database to get stuff done: mail, jobs… so let’s have a look how to… 

PASS SUMMIT 2017 – SQL Server Security

Today is the first day of the PASS SUMMIT 2017 in Seattle (WA). The weather is cloudy and we have only 11°C… but where is the problem? Everything happens inside! (at the Convention Center). In this blog, I will make a summary of main attack vectors against MSSQL environments, based on Argenis FERANDEZ’s session called “Modern Security Attack Vectors Against… 

SQL Server 2016: patching CU with R Services

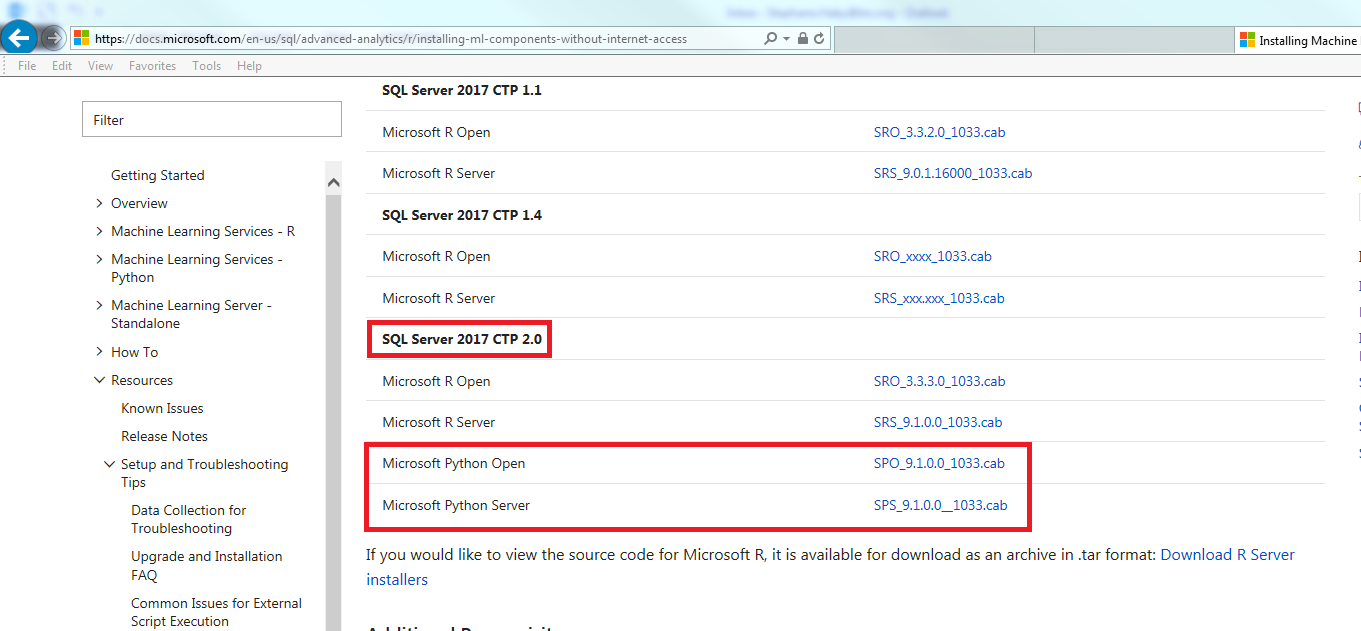
As a good DBA, I begin to be up to date with all Cumulative Update (CU) by my customers. It is the first time that I run an update for SQL Server 2016 with the CU 3. I download the CU on Microsoft website and I begin my patching campaign on all SQL server 2016 instances. The first one is… 

SQL Server 2016: Does Dynamic Data Masking works with INSERT INTO and SELECT INTO commands?

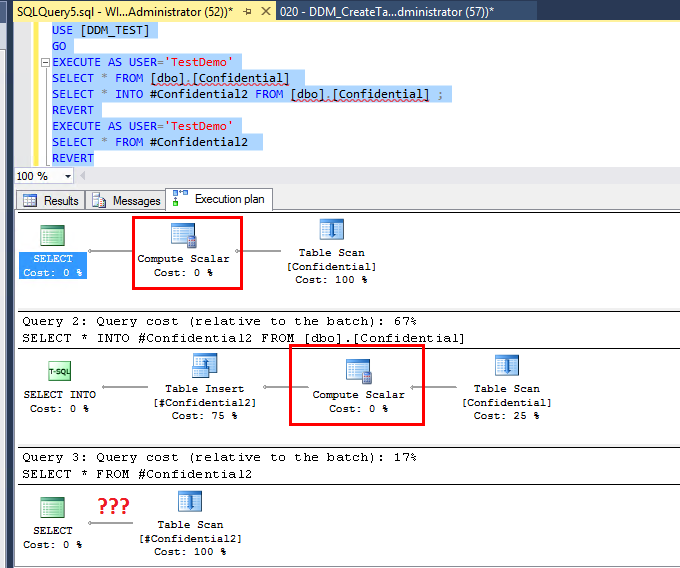
I wonder how works Dynamic Data Masking (DDM) with these two commands INSERT INTO  and SELECT INTO. First, I create a table and add some “sensitive data”: USE [DDM_TEST] GO CREATE TABLE [dbo].[Confidential]( [ID] [int] IDENTITY(1,1) NOT NULL PRIMARY KEY CLUSTERED, [Name] [nvarchar](70)NULL, [CreditCard] [nvarchar](16)NULL, [Salary] [int] NULL, [Email] [nvarchar](60)NULL) insert into [dbo].[Confidential]([Name],[CreditCard],[Salary],[Email]) values (N’Stephane’,N’3546748598467584′,113459,N’[email protected]’) insert into [dbo].[Confidential]([Name],[CreditCard],[Salary],[Email]) values (N’David’,N’3546746598450989′,143576,’[email protected]’)… 

SQL Server 2016: Does Dynamic Data Masking work with Temporal Table?

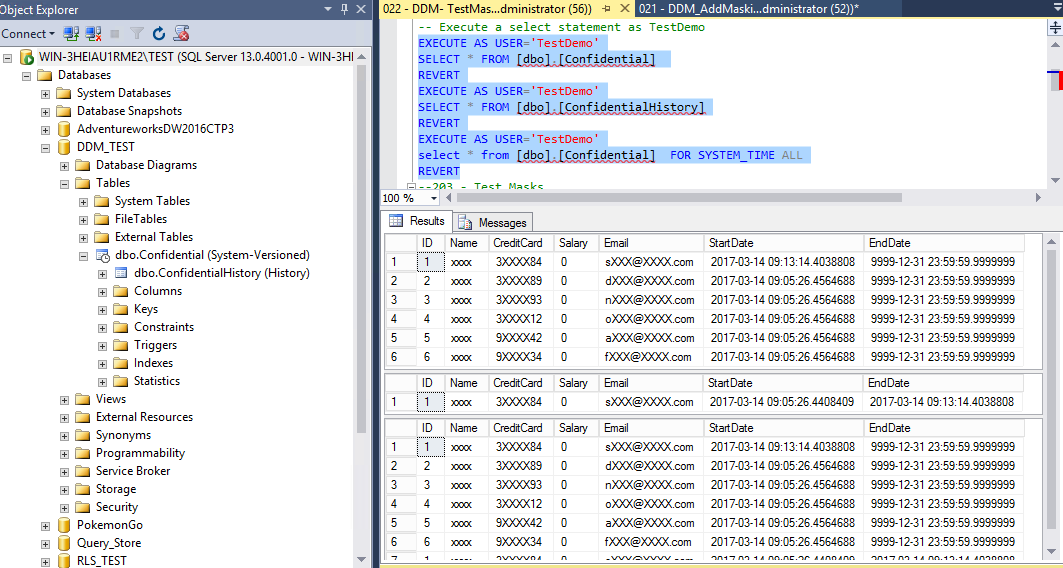
In the last IT Tagen 2016, I presented the Dynamic Data Masking (DDM) and how it worked. To add a little fun, I applied the DDM to a temporal table to see if the history table inherits also from DDM’s rules. In this blog, I explain all the different steps to reproduce my last demo. Step 1: Create the table…