Skip to content

Security

Documentum – RED Warning on D2 after enabling Tomcat HTTP Security Headers

Security is and will always be a very important aspect of IT. Enterprise Content Management (or Document Management Systems or Content Services Platform or whateveryoucallit) is obviously not an exception to that. One of our main goals as a consultant is to add improvements to our customers’ installations for stability, security, and ease of management. However, it happens that not… 

Oracle 21C Security : diagnostics_control and enable diagnostics

By Mouhamadou Diaw Some debug-events and debug-actions are not safe and should be exposed to users with caution. In previous releases, privilege control for the usage of these diagnostics was not sufficient. With Oracle 21c, regular users can be blocked from using these diagnostics to better support separation of duty. Indeed with Oracle 21c, we have a new mechanism to… 

How to find the TLS used for the SQL Server connection

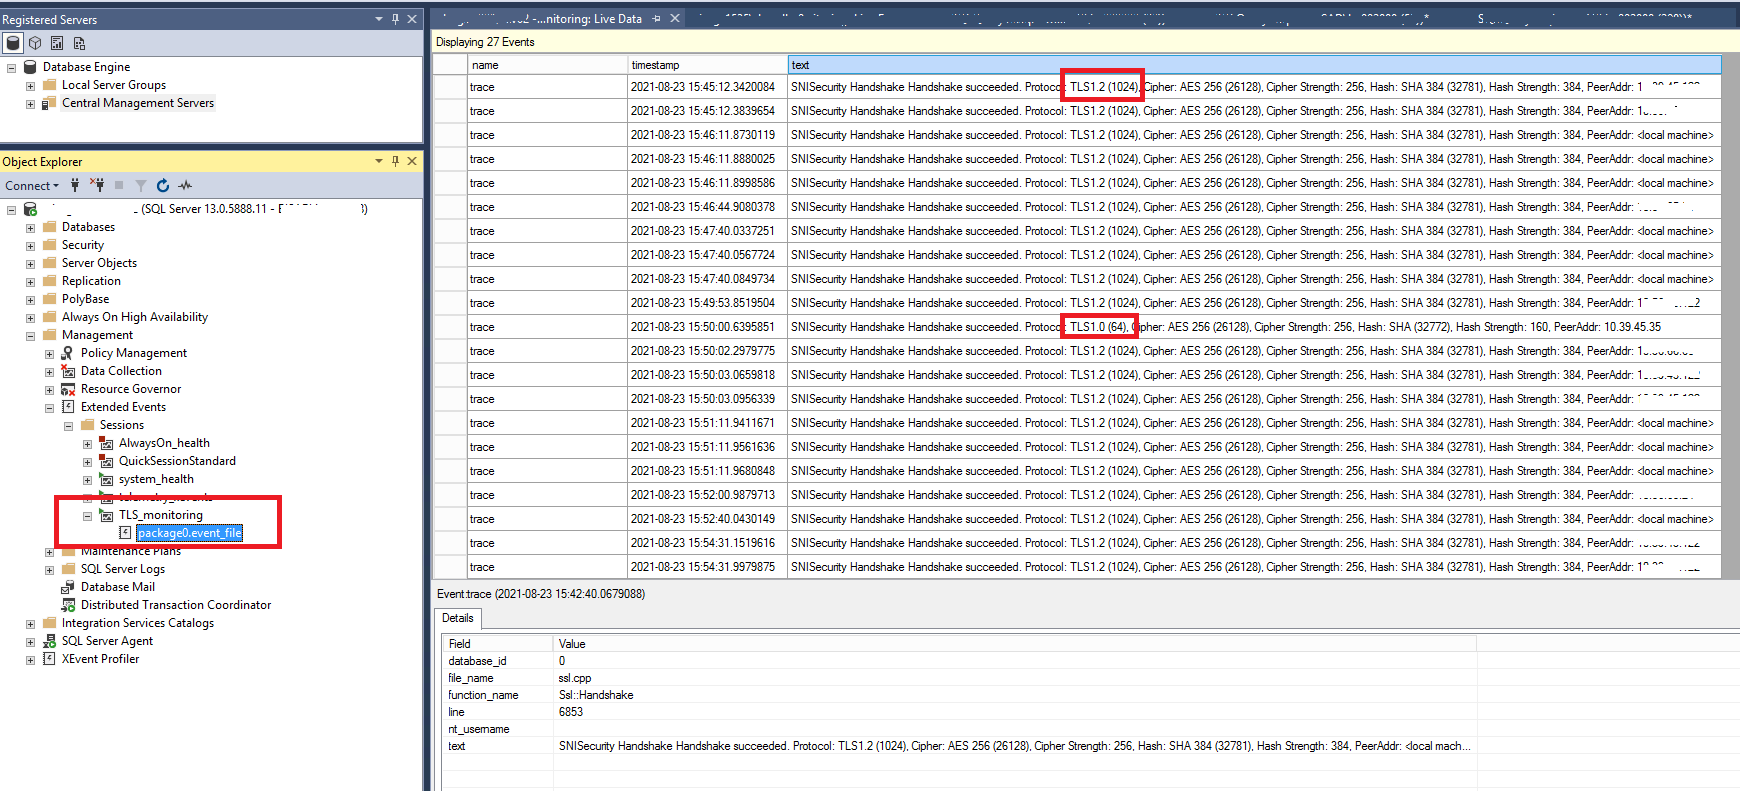
For a customer, I do some research to find which TLS is used on the SQL Server environment. The only way is to create an Extended Event. A big limitation is that the event used is only available on SQL Server 2016 and +. Before use the Built-In Diagnostics (BID) traces. After I implanted the first TLS Monitoring on  a… 

SQL Server: Replace the old SCOM login by the new one

It’s every time hard to replace a login who as role and permissions in every database like the service account for SCOM. In the previous version of Scom, you create a service account (dbiscom) to access the SQL Server and check the health of the databases. Now it’s possible to use the System Center Operations Manager Health Service (NT SERVICEHealthService).… 

Swiss Cyber Security Days (SCSD)

The Swiss Cyber Security Days (SCSD) took place on March 10 and 11, 2021 The largest event in Switzerland entirely dedicated to cyber security took place on March 10 and 11, in a 100% digital form. Despite the health measures related to the coronavirus pandemic, the third edition of the Swiss Cyber Security Days was maintained. Indeed, cyber threats do… 

Oracle 21c: Blockchain Tables

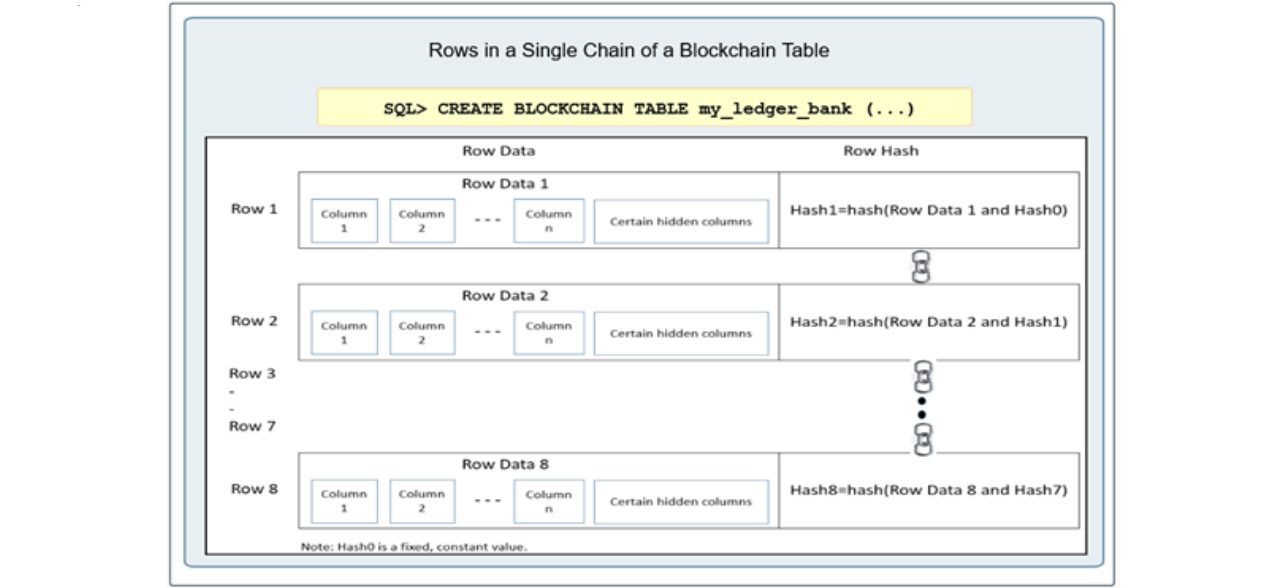
Oracle Blockchain Tables With Oracle Database 20c/21c the new feature Oracle Blockchain Tables has been introduced. Blockchain Tables enable Oracle Database users to create tamper-resistant data management without distributing a ledger across multiple parties. Database security can be improved by using Blockchain Tables to avoid user fraud and administrator fraud as well. One of the main characteristics of Oracle Blockchain… 

Oracle 21c Security : Gradual Database Password Rollover

By Mouhamadou Diaw Starting with Oracle 21c, a password of an application can be changed without having to schedule a downtime. This can be done by using the new profile parameter PASSWORD_ROLLOVER_TIME This will set a rollover period of time where the application can log in using either the old password or the new password. With this enhancement, an administrator… 

Increase your PostgreSQL databases security by checking a few settings Part 2

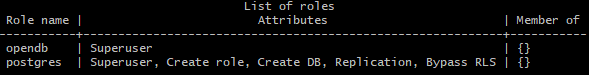
Continuing from my first blog we will check some more access and authentication configurations. Focusing on removing unnecessary database privileges. After that we will configure the backend parameters correctly to have more robust PostgreSQL server/client sessions. And at last SSL encryption for these sessions will be configured. User access and authentication In my previous blog we already setup the pg_wheel… 

Shows output of du command

Increase your PostgreSQL databases security by checking a few settings

This blog provides you with a short overview of easy to control settings that enhance your PostgreSQL security. Mostly by creating a separate group to assign privileged database members. And checking different logging and log rotations settings for better and more secure logging management. In this blog I will go over a few PostgreSQL security settings that help to secure… 

SQL Server Tips: Orphan database user but not so orphan…

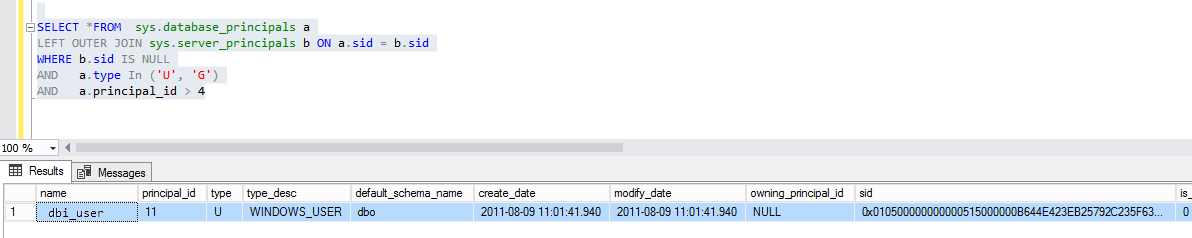
Beginning of this year, it is good to clean up orphan users in SQL Server databases. Even if this practice must be done regularly throughout the year of course. 😉 During my cleaning day, a new case appears that I never had before and enjoy to share it with you. To find orphan database-users, I use this query: SELECT *FROM… 

Using non-root SQL Server containers on Docker and K8s

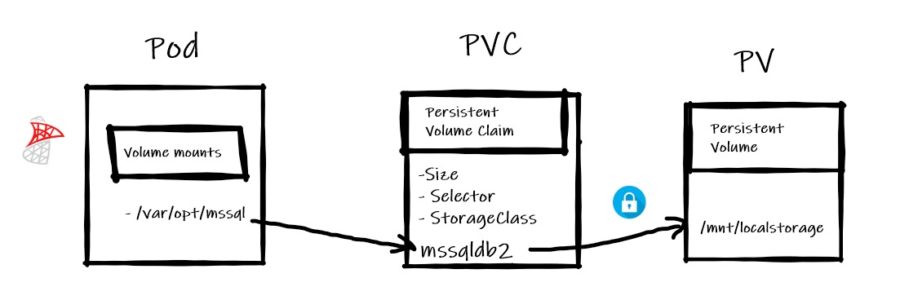
This is something that I waited for a while, in fact since SQL Server 2017 … and the news came out on Wednesday 09th September 2019. Running Non-Root SQL Server Containers is now possible either on the next version of SQL Server (2019) and it has been backported on SQL Server 2017 as well. Non-root SQL Server containers will likely…