Skip to content

encryption

SQL Server Always On Availability Groups and Database Master Keys: A Hidden Failover Pitfall

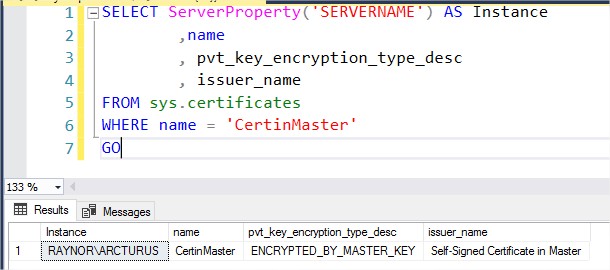
I recently came across an interesting case involving a client whose application used SQL Server symmetric keys to encrypt sensitive data. The database was hosted in an Always On Availability Group environment for high-availability and disaster-recovery. The interesting and challenging aspect of this setup is ensuring that the encryption and decryption remains intact after a failover. This challenge originates from… 

Setting up TLS encryption and authentication in MongoDB

When securing a MongoDB deployment, protecting sensitive data is essential. MongoDB supports encryption throughout the lifecycle of the data, with three primary types of data encryption : Among these, encryption in transit is fundamental : it protects data as it moves between your application and the database. In MongoDB, this is achieved through TLS (Transport Layer Security), which ensures that… 

Documentum – Encrypt BOF passwords with a minimal jar file

Nowadays, with DevOps and containers approaches, you will often see components or software that try to go on a diet, to reduce the size needed to deploy them and therefore the images/containers associated to it. I was recently asked to do something similar on a very specific feature that the Documentum DFC jar files provide: extract and minimize the jar… 

MySQL 8 and Security – Encryption of binary logs

As I discussed in some of my recent talks at conferences (at the DOAG for example), MySQL 8 came out with new features which bring lots of improvements in terms of security. “At-Rest” encryption has been existing from some releases by now: – InnoDB Tablespace Encryption: by 5.7.11 – Redo and Undo Log Data Encryption: by 8.0.1 Now starting from… 

Encryption of shell scripts

In this blog, I will talk about the encryption of files and in particular the encryption of a shell script because that was my use case. Before starting, some people may say/think that you shouldn’t encrypt any scripts and I globally agree with that BUT I still think that there might be some exceptions. I will not debate this further… 

Oracle 12cR2: Online tablespace encryption

By Franck Pachot . By default, all data is visible in the datafiles. Transparent Tablespace Encryption (TDE) can be used to get them encrypted. It requires Enterprise Edition plus Advanced Security Option. Except in the Oracle Cloud when it is available – and mandatory – in all editions. And we can foresee that security policies will be enforced in the… 

Securing your connections to PostgreSQL by using SSL

Security is a big topic today and in the news almost every day. As the database usually holds sensitive data this data must be well protected. In most cases this is done by encrypting critical data inside the database and decrypt only when requested. But this is not all: When a client reads the data it is decrypted inside the… 

Use a wallet to encrypt Oracle client passwords

In our more and more connected world, security is a big concern. Storing password is a very important topic because if a machine is compromised, we can assume that any password stored in clear text are also compromised. I had the question from a customer how can we encrypt the password in our application and monitoring scripts? In this blog… 

Transparent data encryption, key management and backup strategies

Transparent Data Encryption requires the creation of a database key encryption. The database key is a part of the hierarchy of SQL Server encryption tree with at the top of the tree the DPAPI. Then if we traverse the tree from the top to bottom we can find the service master key, the database master key, the server certificate or…